
CYBERCORE UNIVERSAL DEFENSE SYSTEMSENTINEL / 01
F-Droid repository · auto-updates · no account · no trackers
CYBERDROID
Every Cybercore app, one tap, kept up to date.
Add this repository to F-Droid (or Droid-ify, Neo Store) and get Cybercore's privacy-first Android apps with automatic updates. Each APK is the exact signed release published on GitHub, re-verified against its developer certificate before it's listed, and the index itself is signed with a key that never touches GitHub.
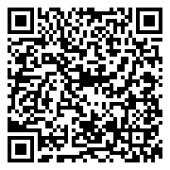
https://cybercoretech.github.io/fdroid/repo
SIGNING FINGERPRINT (SHA-256)
FEATURED PROJECT / ANDROID OPERATIONS
CyberSSH 06 / Blacksite Console
A focused Android SSH client with server fingerprint verification and an operator-controlled remote shell.
01 / In the repository
Our apps,
zero trackers.
Kotlin + Compose on the outside, shared Rust cores where it counts. No ads, no analytics, no accounts. Tap any app for its permissions, screenshots, signer and checksums. This list is built live from the signed repository index.
02 / Latest builds
Fresh off
the signer.
The newest signed builds in the index. Index last signed ….
03 / Trust model
Two signatures,
both checked.
F-Droid verifies the repository index signature on every refresh, and Android verifies every APK update against the developer key it was first installed with. Neither key is stored on GitHub.
RELEASE
Each app is built and signed with its own developer key on the maintainer's machine, then published on GitHub with its SHA-256.
VERIFY
Before listing, every APK's checksum and signing certificate are re-checked against the pin in apps.tsv.
INDEX
fdroidserver builds the index and signs it with the repo key DE37…F3C3.
UPDATE
Your phone checks the index signature, then Android checks the new APK is signed like the installed one.
- Same APKs as GitHub: installing from here, Obtainium or the GitHub release is interchangeable; updates work across all three.
- Self-hosted apps: Holodrive Photos and Nightwatch talk to servers you run (flagged SELF-HOSTED).
- Not the main F-Droid catalog: F-Droid doesn't build these APKs; Cybercore signs them. Main-catalog listings may follow once builds are reproducible.
- Prefer a computer? Each app's README has a verifying
curl … | shinstaller for adb.
04 / Theme matrix
Pick your
signal.
Every Cybercore palette from the shared schema, plus this repository's signature mashups.